
Zimperium researchers reveal a China-linked Android banking trojan that hands a live AI assistant control of infected phones and resists standard removal methods.
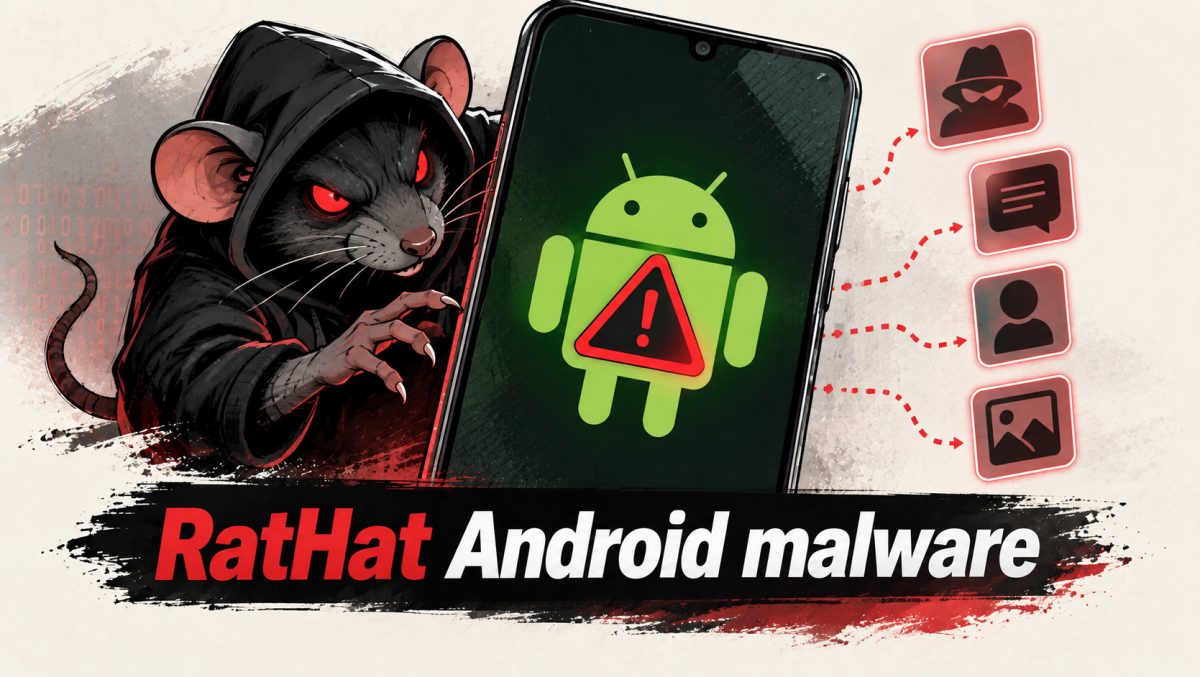
Mobile security firm Zimperium's zLabs research team publicly disclosed a new Android malware family named RatHat in a technical report published on September 16, 2026, describing it as one of the first widely observed cases of generative AI being used operationally inside mobile malware. The malware, assessed to be linked to threat actors operating in China, targets banking and payment app credentials, intercepts one-time passwords and SMS codes, and reconstructs screen-lock PINs and pattern unlocks, while granting attackers persistent shell-level access to infected devices. Security media including CNET, The Hacker News, Malwarebytes and SecurityWeek covered the findings between September 17 and 21, 2026, framing RatHat as a flagship example of AI-driven mobile threats.
Oracle's AI Data Center Bet Is Turning Vertiv and Caterpillar Into Unlikely Winners
How Zimperium Uncovered a New Class of Mobile Threat
Zimperium's blog describes RatHat as a "novel Android malware strain linked to threat actors that appear to be operating in China" that "incorporates novel techniques for persistence and leverages generative AI for operational control." The firm's zLabs team says the malware's defining feature is what it calls "AI-Driven Automation," in which RatHat "uses AI to intelligently navigate and control the device interface in real-time, making its operations more adaptable and harder for security software to detect than traditional, scripted automation."
Follow-up coverage from The Hacker News, Malwarebytes, SecurityWeek and other outlets corroborated the core findings within days. Malwarebytes stated that "RatHat gives a live AI assistant the keys to the accessibility tree of the infected device and uses it to determine where to tap or scroll, rather than following a hardcoded script." SecurityWeek similarly reported that the trojan "relies on generative AI to more intelligently navigate and control the infected devices" and "monitors users' input at the hardware level to reconstruct PIN codes, passwords, and patterns." Attribution to China-based operators rests on infrastructure and behavioral indicators rather than any formal government statement, and no precise infection counts or victim geography have been disclosed publicly as of late September 2026.
How To Check If Motion Assist Reached Your Android 17 Phone
Inside the Attack Chain: From Fake App to Full Device Takeover
According to Zimperium and multiple technical analyses, RatHat spreads outside the official Google Play Store through smishing campaigns and malvertising, using deceptive landing pages that mimic Play Store listings or clone popular apps such as Chrome to push APK downloads. Victims are lured into manually installing the malicious file and granting Accessibility Service permissions, believing they are installing a legitimate update.
Once those permissions are granted, RatHat navigates settings menus to enable Developer Options and Wireless Debugging, then reads the on-screen ADB pairing code to automatically pair with the device's own local Android Debug Bridge daemon, without requiring a connected computer. This sequence escapes Android's normal app sandbox and grants attackers an ADB shell with effectively admin-level control. From there, the malware deploys a Go-based background agent, a proxy or tunneling client for exfiltrating stolen data, and an AI automation module that serializes the live Accessibility tree into a structured format sent to an unnamed popular AI assistant, which identifies on-screen elements and issues navigation commands such as "SCROLL_DOWN," "TAP_BUTTON" or "ENTER_TEXT."
Credential Theft, PIN Reconstruction and the Persistence Problem
Using this AI-guided navigation, RatHat presents credential-stealing overlays that mimic banking and payment apps, intercepts SMS messages and OTP or two-factor codes, and monitors raw touch input at the hardware level to compare coordinates against known keypad and lock-screen layouts, reconstructing PINs and pattern locks even when strong authentication is in use. Reports indicate the malware also logs keystrokes and interactions across other apps, expanding its reach to email accounts and cryptocurrency wallets.
Perhaps the most alarming characteristic, according to multiple advisories, is RatHat's ability to retain access after the visible app appears to be uninstalled. By pairing with local ADB and running native background services, the malware's operators can maintain shell access even after a user deletes the app icon and main package, with some reports describing mechanisms to reinstall deleted components or display fake error dialogs to discourage removal. Malwarebytes warned directly that "if your device is infected with RatHat, you will need to perform a factory reset because its persistence mechanism can survive normal app removal," a recommendation echoed across multiple security advisories covering the malware.
Industry Response and What Comes Next for Android Security
Malwarebytes has added detection under the name Android/Trojan.Exploit.RatHat and is promoting its mobile security product as capable of blocking the trojan and related smishing attempts. Analysts at CNET, BleepingComputer, Infosecurity Magazine and CybersecurityNews have characterized RatHat as an early signal that AI-driven automation could define a new generation of mobile malware capable of adapting faster than traditional scripted threats, since its behavior does not follow a static, predictable pattern that detection tools can easily fingerprint.
Technical advisories consistently urge users to avoid installing apps from third-party sites or links received via SMS, and to treat any unexpected request for Accessibility permissions or prompts to enable Developer Options and Wireless Debugging as red flags. Financial sector commentary recommends that banks and payment providers strengthen defenses against overlay-based and accessibility-linked attacks, including step-up verification triggered when overlays or debugging activity are detected, given that RatHat is explicitly engineered to intercept SMS-based OTPs. No regulatory actions or law enforcement operations tied to RatHat have been publicly reported as of late September 2026, with coverage so far focused entirely on technical analysis and defensive guidance rather than arrests or formal sanctions against the operators.